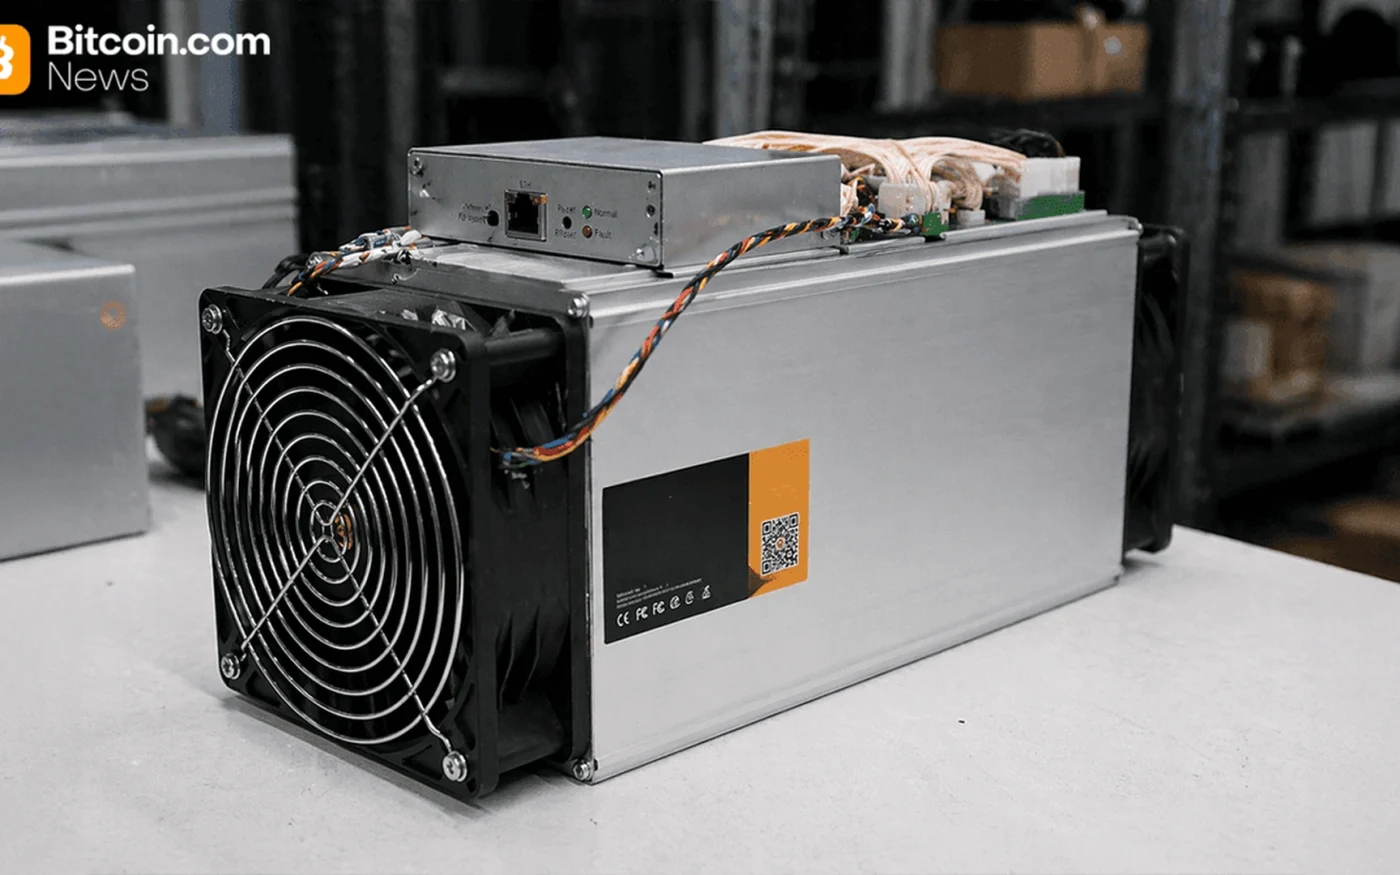
The incident did not steal coins directly from customer wallets. Instead, compromised settings pointed mining machines towards an unauthorised pool, allowing the attacker to receive rewards while affected operators continued paying for electricity and equipment.
Luxor disclosed the incident over the weekend and provided further details on 16 November. The company said its engineers patched the vulnerability within two hours, no customer data was stolen or exposed, and affected clients will be compensated in full.
Redirecting hashrate allowed the attacker to collect mining rewards
Mining income depends on the pool that receives the work performed by the machines. Software that manages many machines can change that destination across an entire group of devices. The equipment may appear to operate normally while its rewards are credited to another account.
Luxor estimated that roughly 13 exahashes per second were affected, representing about $20,000 in mining revenue per hour at the time. A bitcoin address linked to the redirection received about $15,700 in rewards, according to reports based on pool and blockchain data.
Luxor’s claim about the use of AI has not been independently verified
Chief executive Nick Hansen described the compromise as a sophisticated AI-enabled attack, but the company has not publicly explained how artificial intelligence was used or how the initial access was obtained. The claim should therefore be treated as Luxor’s assessment, not as an independently verified technical conclusion.
That distinction matters because AI can have very different roles, including automated searches for weaknesses, creation of phishing messages or assistance with code. Without a detailed technical report, customers cannot yet evaluate which protection failed or whether the same method threatens other mining platforms.
Compensation covers losses but the cause of the attack still requires an explanation
Luxor says the platform named Commander is operating normally and that users do not need to take action. Reimbursement covers direct lost revenue, but mining operators will still want clarity about access records, password and key changes, and alerts capable of detecting a change of mining pool earlier.
The event is a reminder that mining risk extends beyond hardware and energy prices. Centralised management tools improve efficiency, but one compromised system can affect many machines. Operators need alerts for pool changes and independent checks that compare the expected destination of computing power with actual payouts.
This article is for information only and is not investment advice.
 admin_wcContributor · World-CryptMore from